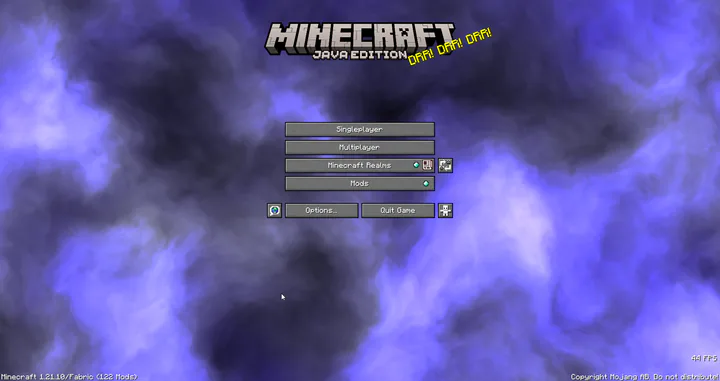
CanvasGLSL
Activea Fabric mod that replaces Minecraft menu backgrounds with custom GLSL shaders. it includes an in-game IDE, syntax highlighting, Shadertoy-compatible uniforms, live compile, and a file manager.
Security research · Computer vision · Small tools
I’m a student developer in Thailand working on security research, computer vision, and small tools built around real friction.
a Fabric mod that replaces Minecraft menu backgrounds with custom GLSL shaders. it includes an in-game IDE, syntax highlighting, Shadertoy-compatible uniforms, live compile, and a file manager.
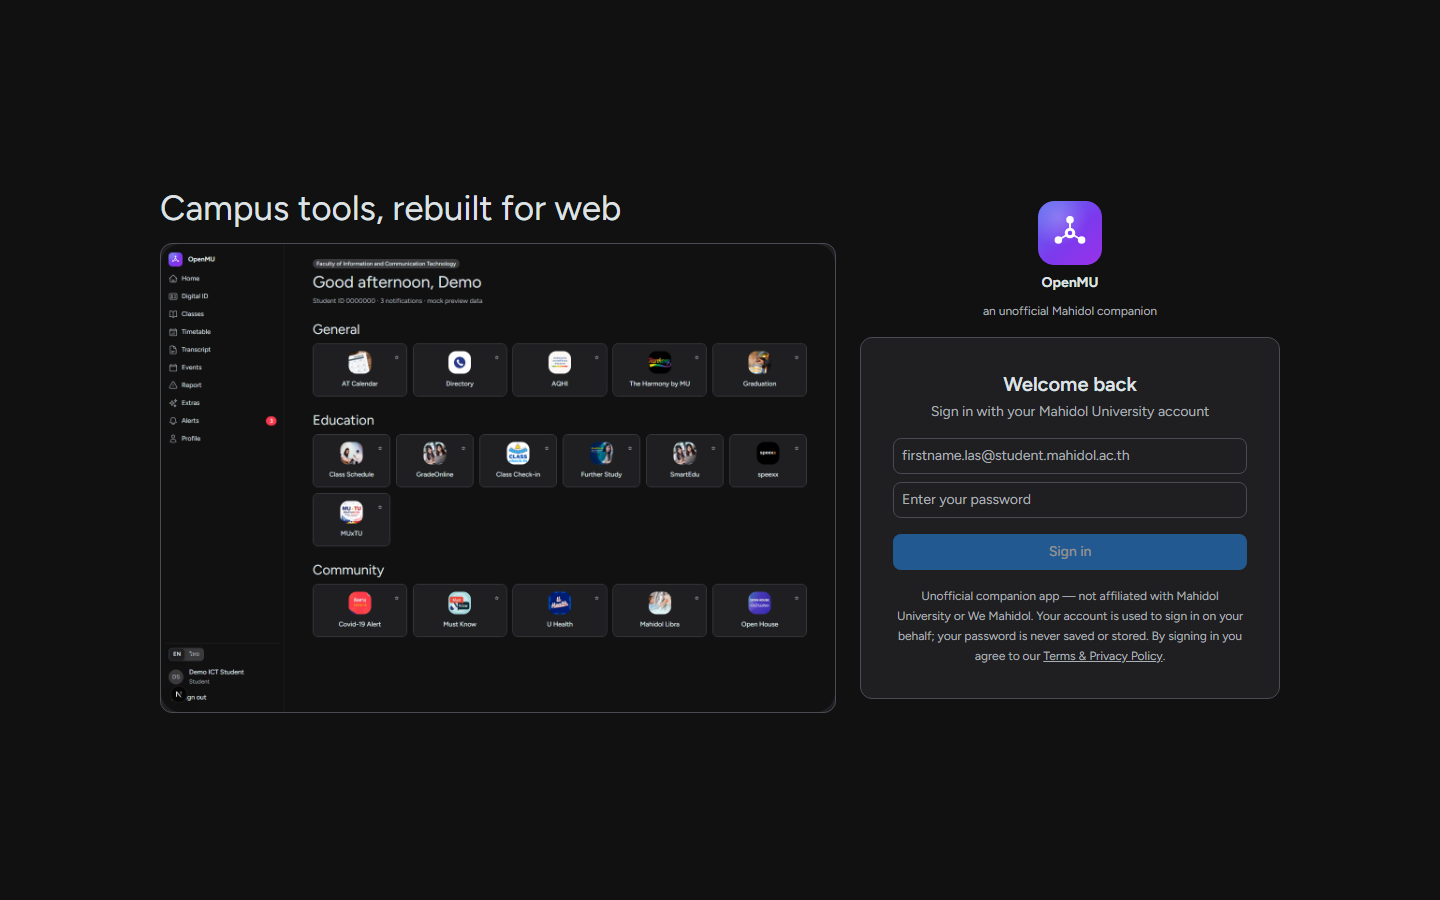
an unofficial, student-built Mahidol companion that brings Digital ID, classes, timetable, transcript, events, alerts, and campus services into one installable web app.
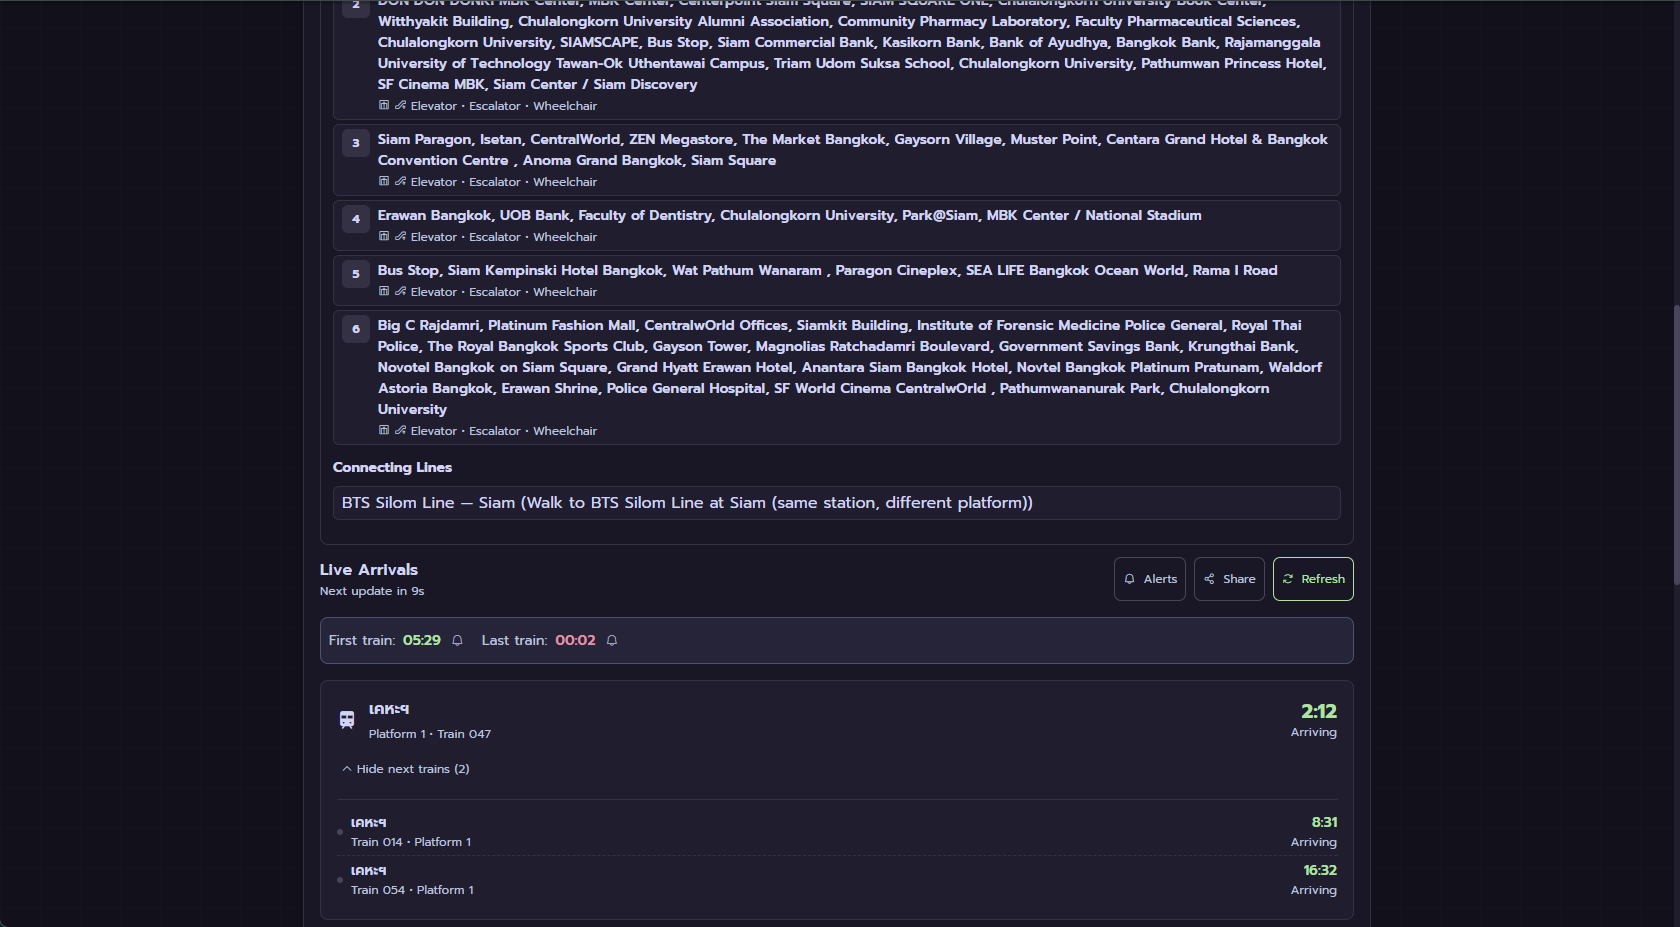
a real-time Bangkok BTS companion with live arrival countdowns, journey planning, fares, station maps, and accessibility details—packaged as a fast installable PWA.
bidirectional bookmark and saved-tab sync across Windows machines, using a private git repository as transport.
a YOLOv11 pipeline that grades corn seed quality from one image against practical defect and USDA damage classes.
cold-chain logistics for Thai agricultural supply chains, with route optimization that batches multi-farmer shipments.
Thai voice interaction for elderly care: medication reminders, emotional support, and emergency alerting.
an authorized review of a multi-tenant education platform where tenant IDs, unsigned cookies, and unauthenticated service APIs were treated as identity. the result was cross-tenant data exposure, exam-integrity failures, and a potential physical-safety risk.
a technical writeup on building a computer-vision pipeline for grading corn kernels by damage type, size consistency, and quality thresholds.
a short field note on the same broken trust boundaries that keep showing up in real systems: weak reset flows, bad CORS, exposed admin panels, and callback bugs.
unauthenticated account takeover on a platform serving international schools. forgot-password endpoint returns the reset token directly in the http response body — four requests, zero prior access, complete staff admin takeover. bonus: open redirect via unvalidated callbackUrl and potential ssrf vector.